
AI doesn’t set its own limits. We do.

About

Legal and technical expertise, working together.

ai42001 helps organisations adopt and manage AI with confidence, bringing governance, legal judgement and technical expertise together. We pair legal, risk and compliance with AI/DevOps and technical implementation — supporting organisations from an initial review of AI use and readiness through to establishing an ISO/IEC 42001 AI Management System.

Our team works on every engagement, connecting business objectives and governance responsibilities with practical controls and technical evidence. That combined approach helps organisations realise AI's opportunities, manage their risks and demonstrate accountable oversight.

Founders

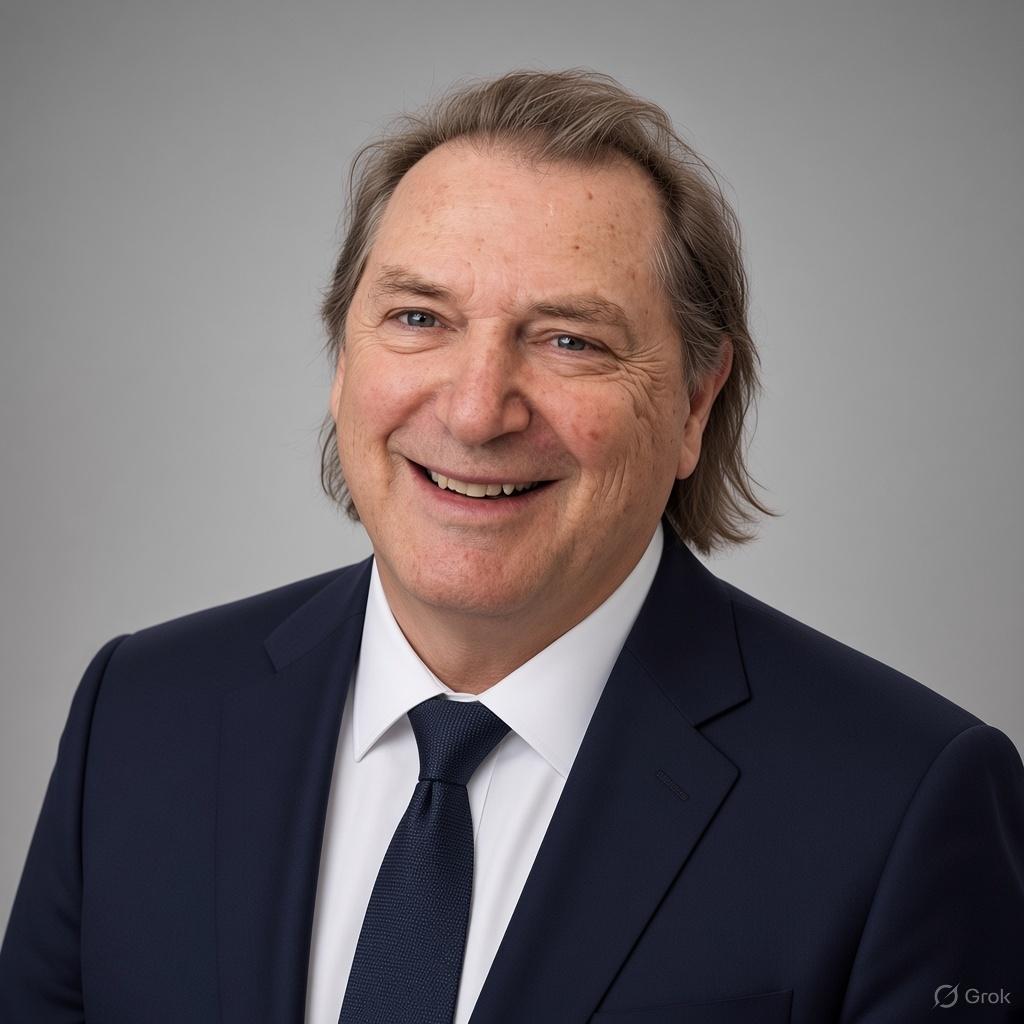
Portrait of Clive Weston

Clive Weston

Dip Law, B.Bus, Grad Dip AppCorpGov

Legal, Risk & Compliance Lead, ai42001

LinkedIn

Clive Weston is the Legal, Risk & Compliance Lead at ai42001, bringing an experienced lawyer’s judgement to AI governance, regulatory compliance and organisational accountability. He helps organisations establish AI Management Systems (AIMS) supported by clear responsibilities, practical controls and legally defensible decisions.

His background in regulated environments informs his approach: interpreting complex requirements, drafting commitments an organisation can fulfil, and supporting governance decisions that withstand scrutiny from boards, regulators and auditors.

On each engagement, Clive leads the legal and governance aspects of the AIMS. His responsibilities include AI policies and supporting procedures, risk and impact assessment methodologies, EU AI Act classification and regulatory mapping, customer and vendor contract provisions, and Data Processing Agreement (DPA) reviews. He also develops the justifications underpinning the Statement of Applicability, connecting control decisions to the organisation’s risks, obligations and operating context.

Clive supports organisations through audit and regulatory review, addressing findings and challenging interpretations where the evidence warrants it. His focus is on proportionate, well-supported compliance that strengthens governance and keeps obligations aligned with applicable requirements.

Owns on every engagement

  • AI governance responsibilities, policies and supporting procedures
  • AI risk and impact assessment methodology
  • Regulatory interpretation, including EU AI Act classification and mapping
  • Review of AI provisions in customer contracts, vendor agreements and Data Processing Agreements
  • Statement of Applicability justifications and responses to audit findings

Credentials & training

  • Legal practitionerExperience interpreting legislation, reviewing contracts and advising on governance and regulatory compliance.
  • AI governance and complianceDeveloping policies, risk assessment approaches and governance frameworks to support Management Systems.
  • Regulated operating modelsRecent work on charitable fundraising, lottery and trade promotion structures, including participant terms, regulatory permissions and interstate requirements.
  • Payment provider compliancePreparing responses to risk and compliance reviews, addressing payment arrangements, customer verification and the legal basis of proposed operations.
  • Contractual and organisational accountabilityTranslating complex requirements into clear obligations, practical procedures and documented positions for external review.

Why the pairing matters

The two halves of ISO 42001 fail separately

ISO/IEC 42001 requires both legally sound governance documentation and demonstrable technical controls, and a team with only one of those skills will produce a management system that fails on the other. The standard's clauses are written in the language of law and management; its Annex A controls are implemented in code, pipelines, and cloud configuration. Bridging them is the entire job.

  • Impact assessments

    Legal
    We design the assessment so it meets the legal tests a regulator applies and doubles as an EU AI Act fundamental-rights assessment input.
    Technical
    We pull the real model performance, subgroup evaluation results, and data lineage that the assessment has to be based on.
  • Human oversight

    Legal
    We define what meaningful human oversight means for your use case, and what your contracts and disclosures commit you to.
    Technical
    We implement it as an enforced checkpoint in the workflow, with an approval record that an auditor can sample.
  • Third-party AI

    Legal
    We review your model vendors' terms, allocate responsibility, and paper the obligations you need flowed down.
    Technical
    We inventory every external model and API your product calls, including the ones added without a procurement review.
  • Audit evidence

    Legal
    We make sure each piece of evidence maps to the clause or control it is meant to satisfy, in the form an auditor accepts.
    Technical
    We automate its generation and collection, so it is current on the day the auditor asks.

How we work

Four commitments

Our team, every engagement
You are not handed to a junior consultant after the sales call. The people you speak with on the first call are the same people who do the work on your account.
We will tell you if you don't need us
Plenty of companies asking about ISO 42001 are 12 months too early. We would rather say so on the first call and keep the relationship than sell you a certification you cannot yet operate.
No template dumps
A generic policy pack will pass a shallow audit and fail the moment a customer or regulator looks closely. Everything we produce is written against your actual AI systems and product strategy.
You own the system when we leave
Every engagement ends with handover: runbooks, training, and a named internal owner who can operate the AIMS without us. The retainer exists because clients want it, not because we built dependency in.

Frameworks we work in

The standards and regulations we map between

Most clients are not solving for one framework. We keep a single control set mapped across all of these, so you answer each question once.

ISO/IEC 42001:2023
AI management systems — the certifiable core of our practice.
EU AI Act
Risk classification, provider and deployer obligations, and Article 17 quality management system mapping.
NIST AI RMF 1.0
Govern, Map, Measure, Manage — commonly requested by US enterprise buyers.
ISO/IEC 27001:2022
Where most of our clients already are; we reuse it rather than duplicate it.
ISO/IEC 23894
AI risk management guidance, used to shape the risk methodology.
SOC 2
Mapped so your existing Trust Services Criteria evidence is reused where it legitimately applies.

Work with us

Our team, on the first call

No account manager, no discovery deck. Thirty minutes with the people who would actually do the work, and an honest answer on whether you need it yet.